JNUC 2026 Day 3 recap
Catch up on JNUC 2026 Day 3: top session themes, the 10 best-attended breakouts, EDU SOTU highlights and more.
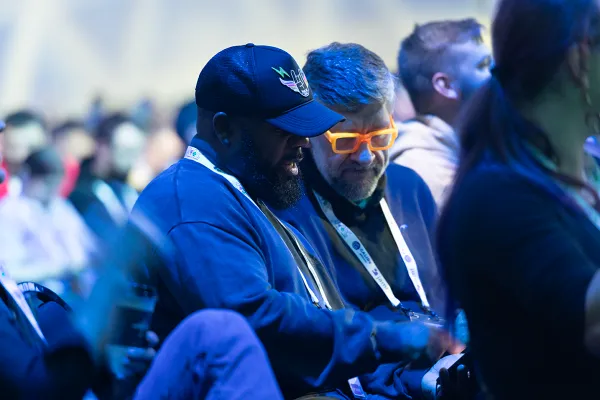
Day 3 of JNUC 2026 was still going strong with Braindates and sessions covering Platform SSO (PSSO), automating your management environment and Declarative Device Management (DDM) as the heart of modern Apple fleet management.
Day 3 themes
- Platform SSO dominates the closing day. Two of the day's best-registered sessions focus on Platform SSO content, making it easily the strongest single theme of the entire conference — nothing on Day 1 or 2 had two sessions clustered this closely together at the top.
- Automation remains a constant thread. A strong automation-focused session continues a pattern that's run through all three days — GitOps and Terraform on Day 1, App Auto Patch on Day 2 and now automation again closing things out.
- DDM's influence persists into the final day. These presentations offered more advanced, forward-looking context than the "getting started" framing that anchored Day 1.
- Zero Trust and fleet visibility round out the day. Security, compliance and device health sessions suggest a secondary thread distinct from the SSO and automation headliners.
Top attended sessions
- Platform SSO: What's New in macOS 27. Chris Scalise, Universal Music Group and Adam Derrick, Jamf previewed the newest Platform SSO capabilities landing in macOS 27, breaking down day-one Jamf support for Apple's latest identity features. The message: get ahead of these changes now so your organization is ready from the start.
- Even MORE Easy Automations with Jamf. Tim Knox and Jesse Dresselhaus of Jamf built live, production-ready automations on stage, from time-limited admin approvals to compliance escalation and Slack integrations. The takeaway: practical, deployable blueprints for self-healing workflows and streamlined onboarding that go well beyond the Jamf console.
- Platform SSO: You're Holding It Wrong. Marc Grubb, Sophos LTD, tackled the identity gap between Mac and Entra ID head-on, making a compelling case for ditching passwords now. His message: phishing-resistant passwordless authentication via passkeys isn't a someday project. The longer admins wait, the more exposed their organizations become.
- Let the Device Decide: DDM Predicate Activations in Practice. Jesse Dresselhaus, Jamf showed how Declarative Device Management predicates let Apple devices evaluate conditions and apply configurations on their own, no server check-in required. With real-world BYOD, shared-device, and field examples, attendees left with practical ways to move beyond Smart Group-driven workflows.
- First Impressions Matter: Building Fast, Secure and Frictionless Zero-Touch Enrollment for macOS. Tim Grebien, Digital Architect Apple/Linux, University of Wolverhampton explores how to design a fast, seamless Zero-Touch enrollment experience for macOS. It covers macOS Setup Assistant decisions, tools like Jamf Setup Manager and Setup Checklist, software deployment timing and Platform SSO integration, providing strategies to balance speed, security and a great first impression.
- OS Updates at a Glance: Visualizing Fleet Health and Compliance at Scale. Topher Nadauld, GRAIL, Inc. and James Mack, Jamf, showed how to turn Smart Groups, Extension Attributes and API data into clear compliance dashboards. Attendees learned to flag devices as Safe, Vulnerable, or Out of Compliance — even accounting for inactive devices — for sharper audits and reporting.
- Extension Attributes: Asking the Right Questions for Better Answers. Ernie Fulton, Fidelity National Financial, showed how to push Extension Attributes further using LaunchDaemons for richer device logging. He also touched on using AI to generate scripts — with a reminder that good results start with asking the right questions and context.
- Zero Touch, Zero Trust: End-to-End App Security with Apple's Managed App Framework. Jedda Wignall and Mark Buffington of Jamf took attendees deep into Apple's ManagedApp framework, showing how Jamf delivers configurations, credentials and device identities straight into managed apps — with zero-touch authentication, Secure Enclave-bound identities and mutual TLS extending hardware trust into every app.
- Modernizing Your Integrations for the Jamf Platform Gateway. Matthew Ward and Chris Ball of Jamf walked through everything shipped on the Jamf Platform APIs since spring 2026 and what it means for integrations built over the years. Attendees left with a practical migration framework and a clear starting point for moving key workflows forward.
- Trust What Jamf Delivers. Block Everything Else. Dan Ritch, Airlock Digital tackled the rising threat of unsanctioned AI agents and ransomware on macOS, showing how Jamf and Airlock Digital pair up to enforce deny-by-default security. Software Jamf delivers is automatically trusted, while approval workflows route through Slack, Teams, or ServiceNow for fast resolution.
Fun fact: Nearly 200 sessions were available across all 3 days. Do you want to rewatch one or weren’t able to attend this year and want to catch up on what was missed? Session recordings will be available on Jamf's YouTube channel approximately 60 days after JNUC
That’s a wrap until next year
From the inspiring keynote to the breakout sessions and Braindates to networking (and celebrating) with the largest (and greatest) community of Mac admins in the world. This year’s JNUC brought together a vibrant community with experts in Apple automation, security and endpoint management — with Jamf as the glue that holds everything and everyone together.
Before we bid adieu to Kansas City, don’t forget to mark your calendars for JNUC 2027, which marks the 25th anniversary of Jamf! Next year’s event will be held in Anaheim, CA on October 26-28th.
Come learn and celebrate with us on the west coast in 2027.